
Download Linux Foundation : CKS Questions & Answers as PDF & Test Software

Last Updated: Nov 17, 2026
No. of Questions: 66 Questions & Answers with Testing Engine
Download Limit: Unlimited
Reliable & Actual Study Materials for CKS Exam Success
Our Online Test Engine & Self Test Software of TestSimulate CKS actual study materials can simulate the exam scene so that you will have a good command of writing speed and time. Then multiple practices make you perfect while in the real Linux Foundation CKS exam. The package practice version will not only provide you high-quality CKS exam preparation materials but also various studying ways.
100% Money Back Guarantee
TestSimulate has an unprecedented 99.6% first time pass rate among our customers.  We're so confident of our products that we provide no hassle product exchange.
- Best exam practice material
- Three formats are optional
- 10 years of excellence
- 365 Days Free Updates
- Learn anywhere, anytime
- 100% Safe shopping experience
- Instant Download: Our system will send you the products you purchase in mailbox in a minute after payment. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
Linux Foundation CKS Practice Q&A's

- Printable CKS PDF Format
- Prepared by CKS Experts
- Instant Access to Download
- Study Anywhere, Anytime
- 365 Days Free Updates
- Free CKS PDF Demo Available
- Download Q&A's Demo
Linux Foundation CKS Online Engine

- Online Tool, Convenient, easy to study.
- Instant Online Access
- Supports All Web Browsers
- Practice Online Anytime
- Test History and Performance Review
- Supports Windows / Mac / Android / iOS, etc.
- Try Online Engine Demo
Linux Foundation CKS Self Test Engine

- Installable Software Application
- Simulates Real Exam Environment
- Builds CKS Exam Confidence
- Supports MS Operating System
- Two Modes For Practice
- Practice Offline Anytime
- Software Screenshots
Linux Foundation CKS Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
Reference: https://training.linuxfoundation.org/certification/certified-kubernetes-security-specialist/#exams
As everyone knows that our Linux Foundation CKS key content materials with high passing rate can help users clear exam mostly. Our passing rate is reaching to 99.49%. We are a professional website selling professional key content about CKS training materials. Through we have PDF version, our main products is selling software products. Most buyers may know that CKS test simulates products are more popular: Online Enging version & Self Test Software version which can simulate the real exam scene. If you want to purchase best CKS Training Materials, we advise you to choose our test simulate products.
However many examinees may wonder the difference between Online Enging version & Self Test Software version and how to choose the version of CKS Test Simulates. Generally speaking, both of them are test engine. Comparing to PDF version which may be printed out and used on paper, these two versions of CKS Test Simulates should be used on electronic device. You can not only obtain the key content materials from CKS Test Simulates but also keep you good mood by simulating the real test scenes and practicing time after time.
Online Enging version of CKS Test Simulates is named as Online enging. As the name suggests, this version should be downloaded and installed on personal computer which should be running on Window and Java System. Some candidates may find CKS Test Simulates unavailable after purchasing. Maybe you should download and run Java system. After finishing payment, Online Enging version of CKS Test Simulates can be downloaded and installed any computer as you like. Our software does not have limits for the quantity of computer and the loading time you will load in. Also after downloading and installing, you can copy CKS Test Simulates to any other device as you like and use it offline.
Self Test Software version of CKS Test Simulates can simulate the real test scenes like Online enging version. The difference from Online enging is that it can be used on any device because it is operating based on web browser. If you are Mac computer or if you want to use on Mobile phone or IPad, you should choose Self Test Software version of CKS Test Simulates. Normally it should be operating online for the first time, if you do not clear cache, you can prepare CKS Key Content offline the second times.
The test engine is a progressive study tool which is useful and convenient for learners so that our CKS test simulates is acceptable for most buyers. Of course, if you get used to studying on paper, PDF version has same key contest materials of CKS. Besides, we provide excellent before-sale and after-sale service support for all learners who are interested in our CKS training materials. 7*24*365 online service: you don't need to worry about time difference or different holidays as our customers are from all over the world. You can always get our support aid in time. If you want to know more service terms about Linux Foundation CKS Key Content materials like our "365 Days Free Updates Download" and "Money Back Guaranteed", we are pleased to hear from you any time.
Linux Foundation Certified Kubernetes Security Specialist (CKS) Sample Questions:
SIMULATION
use the Trivy to scan the following images,
1. amazonlinux:1
2. k8s.gcr.io/kube-controller-manager:v1.18.6
Look for images with HIGH or CRITICAL severity vulnerabilities and store the output of the same in /opt/trivy-vulnerable.txt
Correct Answer:
Send us you rsuggestion on it
SIMULATION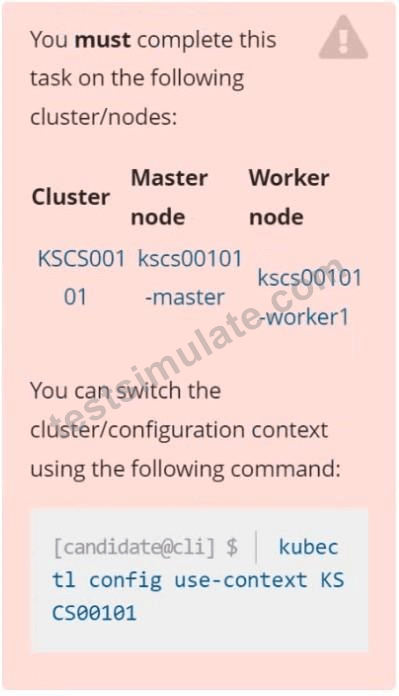
Context
A default-deny NetworkPolicy avoids to accidentally expose a Pod in a namespace that doesn't have any other NetworkPolicy defined.
Task
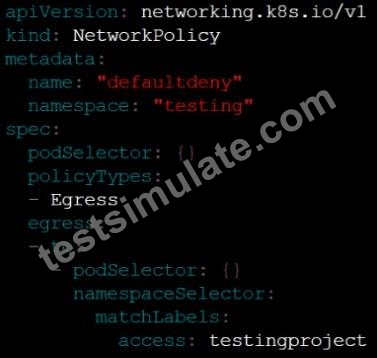
Create a new default-deny NetworkPolicy named defaultdeny in the namespace testing for all traffic of type Egress.
The new NetworkPolicy must deny all Egress traffic in the namespace testing.
Apply the newly created default-deny NetworkPolicy to all Pods running in namespace testing.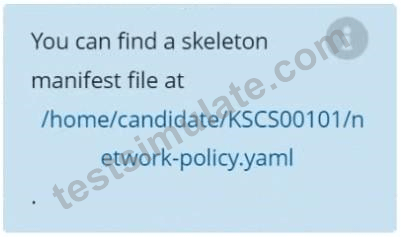
Correct Answer:
See the Explanation below
Explanation: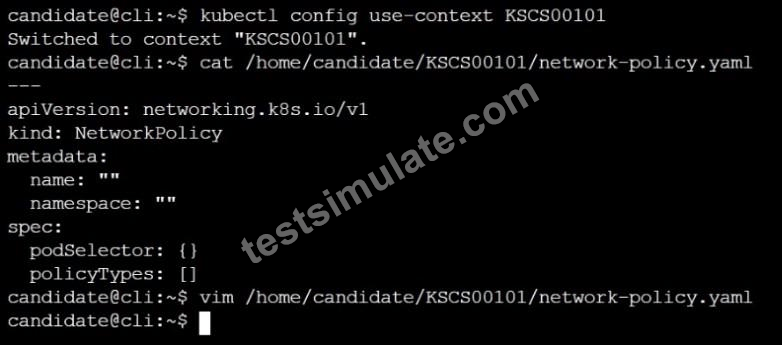
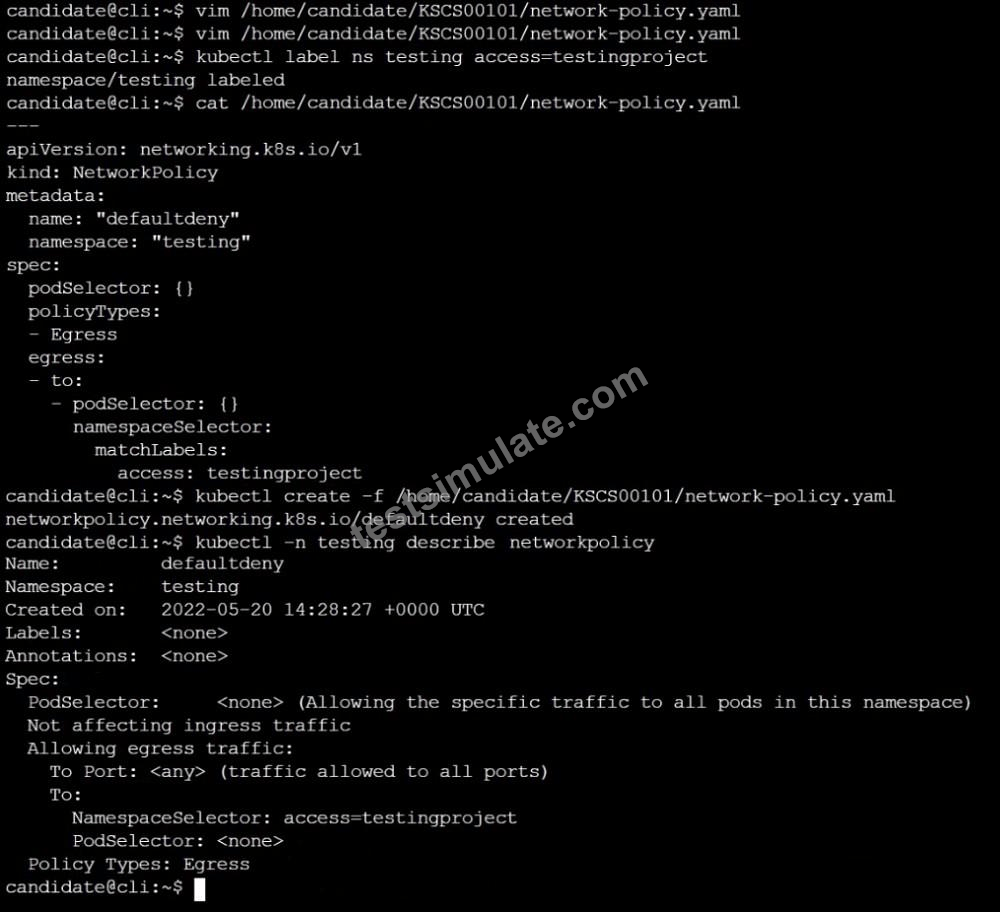
SIMULATION
You must connect to the correct host . Failure to do so may
result in a zero score.
[candidato@base] $ ssh cks000023
Task
Analyze and edit the Dockerfile located at /home/candidate/subtle-bee/build/Dockerfile, fixing one instruction present in the file that is a prominent security/best-practice issue.
Do not add or remove instructions; only modify the one existing instruction with a security/best-practice concern.
Do not build the Dockerfile, Failure to do so may result in running out of storage and a zero score.
Analyze and edit the given manifest file /home/candidate/subtle-bee/deployment.yaml, fixing one fields present in the file that are a prominent security/best-practice issue.
Do not add or remove fields; only modify the one existing field with a security/best-practice concern.
Should you need an unprivileged user for any of the tasks, use user nobody with user ID 65535.
Correct Answer:
See the Explanation below for complete solution
Explanation:
0) Connect to the correct host
ssh cks000023
sudo -i
PART A - Fix ONE prominent Dockerfile security/best-practice issue
1) Open the Dockerfile
vi /home/candidate/subtle-bee/build/Dockerfile
2) Find the "most obvious" security/best-practice problem and modify ONLY THAT ONE instruction Use / search in vi to quickly find candidates:
Candidate 1 (very common): USER root (or no USER but a USER 0)
Search:
/USER
If you see:
USER root
Change that single instruction to:
USER 65535
(or USER nobody if that exact word is already used in the file-but the task explicitly allows UID 65535, so USER 65535 is safest.)
✅ This is one-instruction change and is a top-tier best practice.
Candidate 2 (very common): FROM <image>:latest
Search:
/FROM
If you see something like:
FROM nginx:latest
Change ONLY that line to a pinned tag (example):
FROM nginx:1.25.5
(Any non-latest pinned version is the point. Don't add a digest line; just modify the existing FROM line.) Candidate 3: ADD http://... (remote URL download) Search:
/ADD
If you see remote URL usage like:
ADD https://example.com/app.tar.gz /app/
Change that single instruction to COPY only if it's copying local files.
If it's a remote URL, the more "correct" fix would normally be using curl with verification, but that would require adding instructions (not allowed).
So in this exam constraint, do NOT pick this unless it's actually a local add like:
ADD . /app
Then change just the word:
COPY . /app
3) Save and exit
:wq
Don't run docker build (task forbids building).
PART B - Fix ONE prominent security/best-practice issue in the Deployment manifest
4) Open the manifest
vi /home/candidate/subtle-bee/deployment.yaml
5) Change ONLY ONE existing field that is a clear security issue
Use / search in vi for the usual "bad fields":
Option 1 (most common): running as root
Search:
/runAsUser
If you see:
runAsUser: 0
Change that one existing field value to:
runAsUser: 65535
✅ This is a single-field change and matches the prompt hint.
Option 2: privileged container
Search:
/privileged
If you see:
privileged: true
Change only that value to:
privileged: false
Option 3: allow privilege escalation
Search:
/allowPrivilegeEscalation
If you see:
allowPrivilegeEscalation: true
Change only that value to:
allowPrivilegeEscalation: false
Option 4: writable root filesystem
Search:
/readOnlyRootFilesystem
If you see:
readOnlyRootFilesystem: false
Change only that value to:
readOnlyRootFilesystem: true
Option 5: image uses :latest
Search:
/image:
If you see:
image: something:latest
Change only that value to a pinned tag, e.g.:
image: something:1.2.3
6) Save and exit
:wq
What to pick (fast decision rule)
If you see run as root in either file, that's usually the highest scoring / most "prominent" security issue.
Dockerfile: USER root → USER 65535
Deployment: runAsUser: 0 → runAsUser: 65535
Those are perfect because you only modify one line/field and it matches the hint.
SIMULATION
Create a network policy named allow-np, that allows pod in the namespace staging to connect to port 80 of other pods in the same namespace.
Ensure that Network Policy:-
1. Does not allow access to pod not listening on port 80.
2. Does not allow access from Pods, not in namespace staging.
Correct Answer:
See the Explanation belowExplanation:
apiVersion: networking.k8s.io/v1
kind: NetworkPolicy
metadata:
name: network-policy
spec:
podSelector: {} #selects all the pods in the namespace deployed
policyTypes:
- Ingress
ingress:
- ports: #in input traffic allowed only through 80 port only
- protocol: TCP
port: 80
SIMULATION
Context
For testing purposes, the kubeadm provisioned cluster 's API server
was configured to allow unauthenticated and unauthorized access.
Task
First, secure the cluster 's API server configuring it as follows:
. Forbid anonymous authentication
. Use authorization mode Node,RBAC
. Use admission controller NodeRestriction
The cluster uses the Docker Engine as its container runtime . If needed, use the docker command to troubleshoot running containers.
kubectl is configured to use unauthenticated and unauthorized access. You do not have to change it, but be aware that kubectl will stop working once you have secured the cluster .
You can use the cluster 's original kubectl configuration file located at etc/kubernetes/admin.conf to access the secured cluster.
Next, to clean up, remove the ClusterRoleBinding
system:anonymous.
Correct Answer:
See the Explanation below for complete solution
Explanation:
1) SSH to control-plane node
ssh cks000002
sudo -i
2) Edit API Server static pod manifest
API server in kubeadm runs as a static pod.
vi /etc/kubernetes/manifests/kube-apiserver.yaml
3) Apply required API Server security settings
3.1 Forbid anonymous authentication
Find command: section and ensure this line exists:
- --anonymous-auth=false
3.2 Use authorization mode Node,RBAC
Ensure exactly this line exists (and no AlwaysAllow):
- --authorization-mode=Node,RBAC
❌ Remove if present:
- --authorization-mode=AlwaysAllow
3.3 Enable admission controller NodeRestriction
Find --enable-admission-plugins and ensure NodeRestriction is included.
Correct example:
- --enable-admission-plugins=NodeRestriction
If other plugins already exist, append NodeRestriction, e.g.:
- --enable-admission-plugins=NamespaceLifecycle,ServiceAccount,NodeRestriction
4) Save file and let kubelet restart API server
Just save and exit (:wq)
Kubelet will automatically restart the API server pod.
5) Switch kubectl to secured config
Current kubectl will stop working after API server hardening.
export KUBECONFIG=/etc/kubernetes/admin.conf
Verify access:
kubectl get nodes
6) Remove insecure ClusterRoleBinding
Delete system:anonymous binding:
kubectl delete clusterrolebinding system:anonymous
Verify removal:
kubectl get clusterrolebinding | grep anonymous
(no output = correct)
7) Quick validation (optional but fast)
API server flags check:
grep -n "anonymous-auth" /etc/kubernetes/manifests/kube-apiserver.yaml
grep -n "authorization-mode" /etc/kubernetes/manifests/kube-apiserver.yaml grep -n "NodeRestriction" /etc/kubernetes/manifests/kube-apiserver.yaml
Viewing page 1 out of 14 pages.
Viewing questions 1-5 out of 66 questions.
 Stephanie
Zoe
Aubrey
Brian
Darcy
Fitzgerald
Hugo
TestSimulate is the world's largest certification preparation company with 99.6% Pass Rate History from 74352+ Satisfied Customers in 148 Countries.

Over 74352+ Satisfied Customers


